Router Hardening Checklist: 15 Steps to Lock Down Your Router
Router hardening means changing default settings and disabling unneeded features so the device that guards your network is not its weakest point. The most important actions are changing default credentials, updating firmware, disabling remote administration, and using strong Wi-Fi encryption.
Work through this checklist in order; each step takes only a few minutes.
Secure administrative access
- Change the default admin username and password. Default credentials are publicly documented for most models. Use a unique, long password stored in a password manager.
- Disable remote administration. Management pages should be reachable only from inside your network. If remote access is truly required, use a VPN to reach the internal network first.
- Use HTTPS for the admin interface if the option exists, and disable plain HTTP and Telnet.
- Restrict who can log in. Where supported, limit admin access to specific internal addresses or a management VLAN.
- Set a session timeout so an unattended admin session does not remain open.
Keep the firmware current
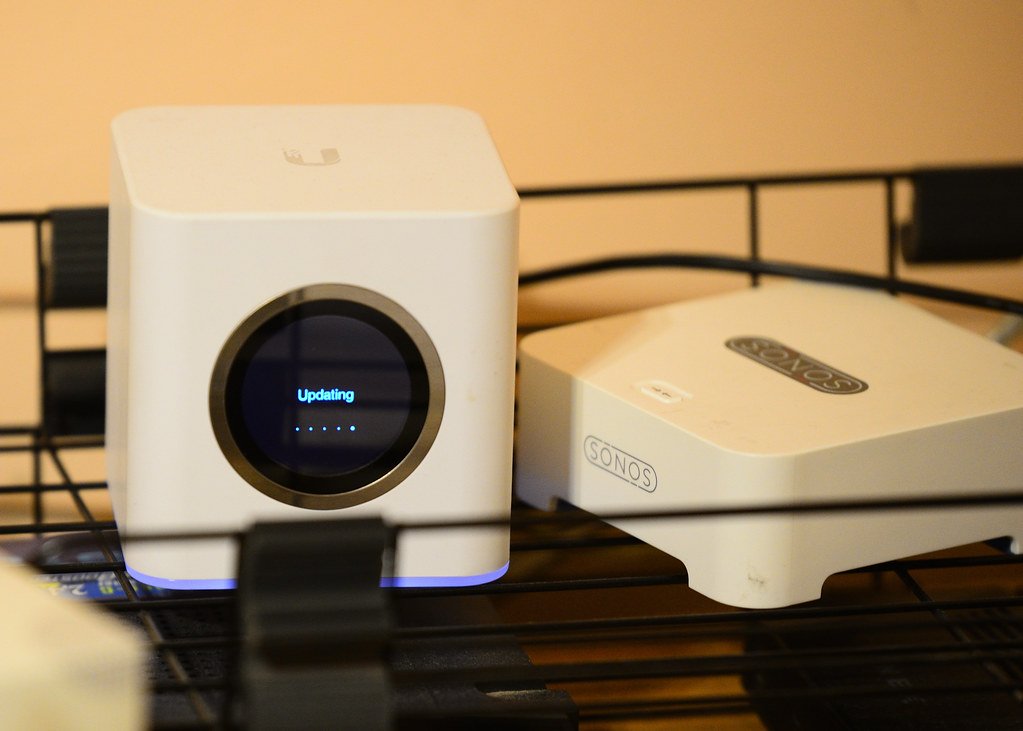
- Check for firmware updates now, then regularly. Router firmware fixes security flaws that attackers actively exploit. If automatic updates are available, enable them.
- Replace unsupported devices. If the manufacturer no longer issues updates for your model, it will accumulate unfixed vulnerabilities. Plan a replacement rather than hoping for the best.
Lock down Wi-Fi
- Use WPA3 or WPA2 with AES. Avoid WEP and TKIP completely.
- Choose a strong Wi-Fi passphrase, different from the admin password.
- Disable WPS. Its PIN-based setup has known weaknesses.
- Enable a guest network with client isolation, and give visitors and smart devices that network instead of your main one.
Reduce the attack surface
- Turn off services you do not use. Universal Plug and Play (UPnP) can let internal software open ports to the internet automatically; disable it unless an application truly needs it. Also disable unused file-sharing, FTP, and remote-access features built into the router.
- Audit port forwarding. Remove any rule you do not recognize or no longer need. Each forwarded port exposes an internal service to the internet.
- Confirm the firewall is enabled and set to block unsolicited inbound traffic. Consider enabling a stateful inspection option if offered.
Monitor and recover
- Enable logging and review connected devices. Check the client list occasionally for unfamiliar devices. If logs can be sent to another system, do so.
Also back up the router configuration after hardening so you can restore quickly, and store that file securely because it may contain sensitive settings.
DNS and extra protections
Consider setting the router to use a trusted DNS resolver that supports encrypted queries and malicious-domain filtering. This helps protect every device on the network at once. If your router supports it, create separate networks for IoT equipment, which tends to be patched less often.
What to do if you suspect compromise
Signs include unexplained DNS changes, unknown admin accounts, settings reverting, or unusually slow connections. Perform a factory reset, update firmware before reconnecting to the internet if possible, set new credentials, then reconfigure from scratch rather than restoring an old backup that may carry malicious settings. Change passwords for accounts you accessed while the router may have been compromised.
Making hardening a habit
Hardening is not a one-time event. Put a recurring reminder in your calendar every three months to do a short review: confirm the firmware version, glance at the list of connected devices, check port forwarding and UPnP mappings, and verify that remote administration remains off. Keep a note of the settings you changed and why, so that after a reset or router replacement you can reproduce the secure configuration quickly.
For small businesses, add two more habits. First, record who has the administrator password and rotate it when that person leaves. Second, keep the router in a location where unauthorized people cannot press its reset button or plug into its ports. Physical access is often overlooked but can bypass many software protections.
Why attackers target routers
Routers are attractive because they are always on, sit at the boundary of the network, rarely run security software, and are often left unpatched for years. A compromised router lets an attacker watch unencrypted traffic, redirect DNS requests to fake sites, or use the device as a relay for attacks on others. Because the owner usually sees nothing wrong, the compromise can last a long time. That combination of high value and low visibility is exactly why a short hardening session pays off.
Router settings for small offices
Offices should go a step further than households. Use a business-grade router or firewall that receives regular security updates, create separate networks for staff, guests, and devices, and send logs to a central place. Assign administration to named accounts rather than a shared login, and review the configuration after any staff or provider change. If an external provider manages your equipment, ask in writing how often it is updated and who can access it remotely.
Frequently asked questions
How often should I update router firmware?
Check at least every few months, or enable automatic updates if available. Apply critical security updates as soon as they are released.
Is it safe to leave UPnP enabled?
It is convenient but risky, because any software on your network can request open ports. Disable it and forward specific ports manually if a service needs them.
Should I use the router provided by my internet provider?
It can be fine if it receives updates and lets you change key settings. If it restricts configuration or is unsupported, consider using your own router behind it.
Key takeaways
- Change default credentials and disable remote administration first.
- Firmware updates are essential; replace devices that no longer receive them.
- Use WPA3 or WPA2-AES, disable WPS, and isolate guests and IoT devices.
- Disable UPnP and audit port forwards to reduce exposure.